What does zero-trust security look like when it keeps pace with AI, virtual machine, and Kubernetes workloads? This blog post shows how VMware vDefend™ for VCF 9.1 applies a unified zero-trust model that reduces lateral attack risk while maintaining the performance modern applications demand. Read the blog to see how VMware helps you strengthen security without added complexity.
What is VMware vDefend for VCF 9.1 and why does it matter for AI workloads?
VMware vDefend for VCF 9.1 is a zero-trust lateral security solution that is built directly into VMware Cloud Foundation (VCF). It is designed to protect modern distributed workloads—including AI, high-performance computing, VMs, containers, and Kubernetes—without sacrificing performance.
As enterprises deploy AI agents and AI workloads across private clouds that span both VMs and Kubernetes, the attack surface grows and becomes more dynamic. Traditional perimeter-only security is no longer enough, especially as attackers increasingly use AI-assisted, semi-autonomous techniques and operate at machine speed.
vDefend helps organizations:
- Reduce lateral movement risk by enforcing zero-trust lateral security inside the infrastructure, not just at the perimeter.
- Apply consistent security across VMs, Kubernetes (VKS), and even bare-metal workloads using a single policy model and console.
- Keep up with AI-scale performance needs through high-performance threat prevention, including a new IDPS Turbo Mode that increases throughput from 3 Gbps to 9 Gbps per host and up to 9 Tbps per VCF domain.
- Consolidate security into the core VCF platform instead of relying on fragmented point tools.
Because vDefend is hypervisor-native and distributed, it provides a closed-loop security architecture where policies are created once and automatically enforced as workloads are created or moved. This helps security teams match the speed of modern AI and cloud-native deployments while maintaining a zero-trust posture.
How does vDefend 9.1 simplify and automate lateral security for tenants and admins?
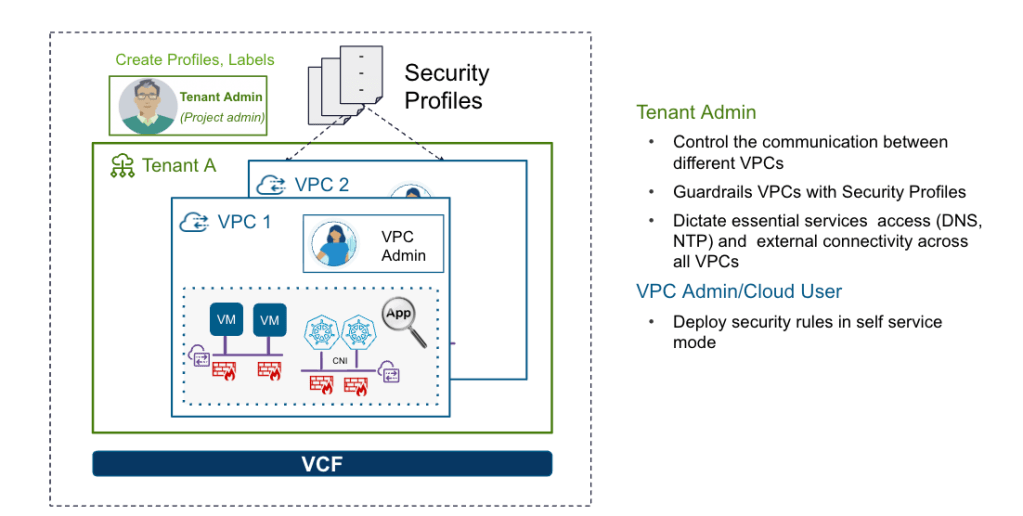
vDefend 9.1 introduces a self-service security model tightly integrated with VCF Automation so that both central teams and tenant admins can work more efficiently.
Key capabilities include:
- Self-Service Lateral Security with VCF Automation
Infrastructure and security teams can define guardrails—such as predefined VPC security profiles and delegated Distributed Firewall (DFW) settings—so tenant admins can safely consume security features on demand. This supports faster application onboarding while maintaining a consistent baseline.
- VPC Simplified Security
Tenant admins can apply one-click security profiles to new or existing Virtual Private Clouds (VPCs). This automatically sets the default security posture and removes the need to manually build foundational DFW rules.
- System-defined vs. user-defined policies
Per-VPC system-defined DFW rules are not editable, ensuring guardrails stay intact. User-defined policies are evaluated first, followed by system-defined VPC policies, giving teams flexibility within a controlled framework.
- Granular firewall control
The release adds more granular control for both Distributed and Gateway Firewalls, including automated orchestration using Privileged Labels to streamline policy management.
The result is a model where central teams define the security framework once, and tenant admins can operate within that framework without opening gaps. This helps organizations scale lateral security consistently across many tenants and applications.
How does vDefend 9.1 protect both VMs and Kubernetes workloads at scale?
vDefend 9.1 is designed to provide unified lateral threat prevention across VMs and Kubernetes, which is critical as AI and cloud-native adoption accelerates.
Key capabilities include:
- Unified IDS/IPS for VMs and VKS
vDefend extends its hypervisor-native IDS/IPS from VMs to vSphere Kubernetes Service (VKS) workloads via CNI integration. Security teams can enable IDS/IPS at the pod level, continuously inspecting traffic and blocking threats on mixed-mode hosts (VMs and Kubernetes) using a single console and policy model.
- Compliance and virtual patching
Customers use IDS/IPS to help meet PCI-DSS and HIPAA requirements and to implement virtual patching—protecting against software vulnerabilities while official patches are rolled out.
- High-performance threat prevention with Turbo Mode
The new IDPS Turbo Mode delivers a 3x throughput increase, from 3 Gbps to 9 Gbps per host and up to 9 Tbps per VCF instance. This supports AI and high-capacity workloads that generate large volumes of east-west traffic.
- Traffic optimization with exempt actions
Security admins can define exempt actions to exclude trusted flows—such as nightly backups—from inspection, improving efficiency without weakening security.
- Enhanced Distributed Firewall with L7 visibility
A 5x increase in Application Identification adds about 4,000 new Application IDs. This gives teams deeper Layer 7 visibility and lets them write granular firewall rules based on specific applications, not just ports and protocols.
- Federated identity-based firewalling
Identity-based firewalling now works across multi-site (federated) environments, enabling consistent policy enforcement in large, distributed deployments.
Together, these features help organizations reimagine lateral security for AI-era infrastructure—delivering consistent, high-performance protection across VMs, containers, and Kubernetes workloads inside VMware Cloud Foundation.


 Sign in with LinkedIn